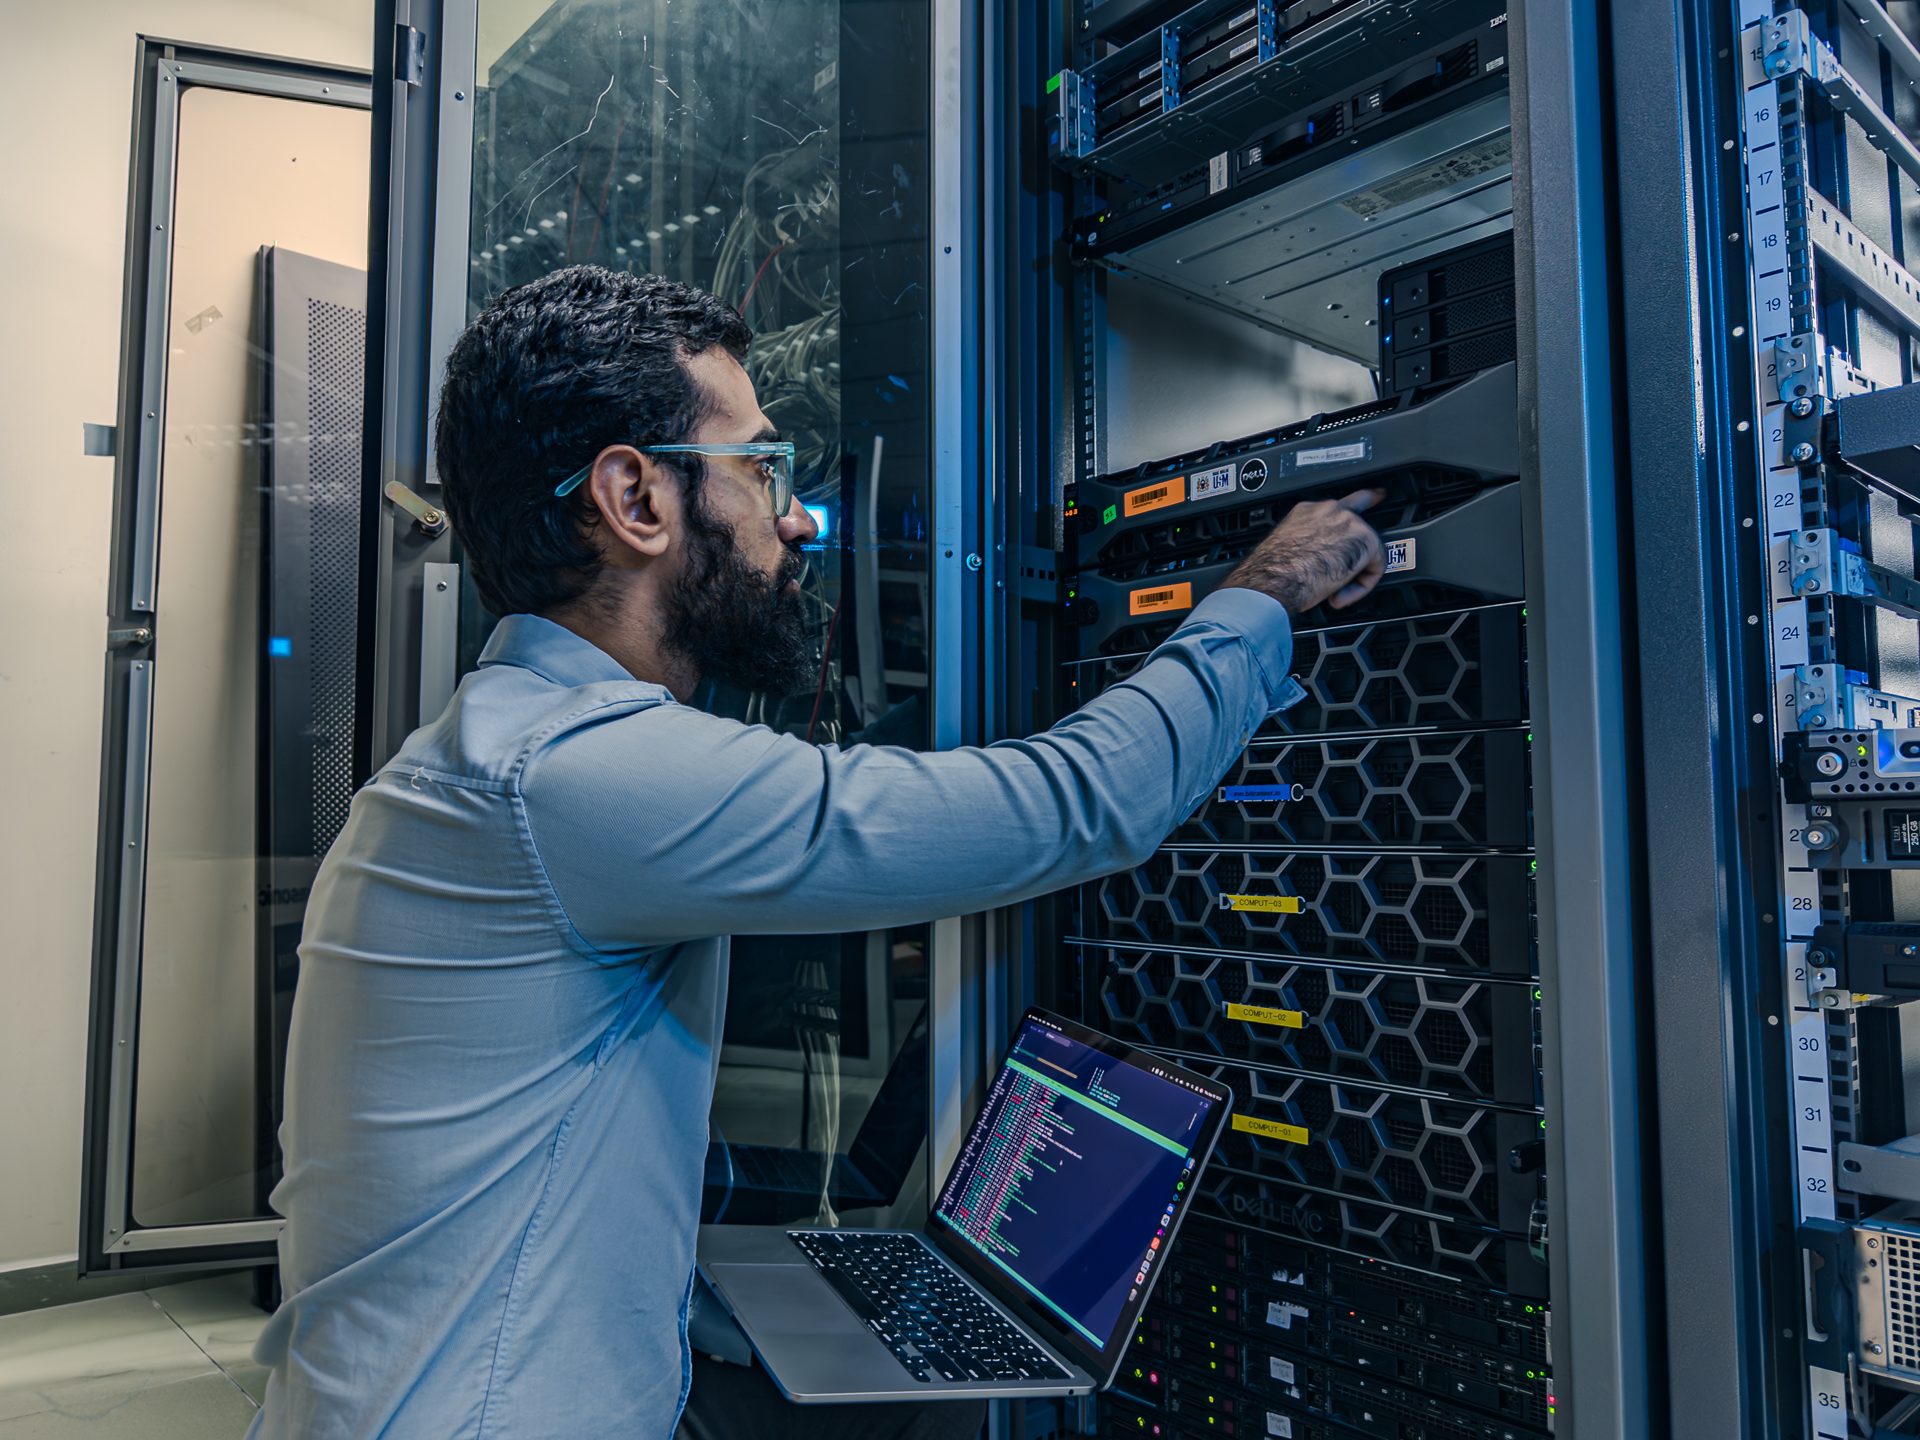
A strong security posture requires more than automated vulnerability scans. A professional pentest service uses controlled attack techniques to validate whether weaknesses in your systems can actually be exploited and what business impact could follow. The objective is not simply to identify vulnerabilities, but to validate whether they can be chained together and what real business impact they could create, such as access to a customer database or takeover of an administrative account.
Who Needs Penetration Testing
SMEs that need certified third-party testing for customer contracts or insurance, GLCs operating critical public services, and government agencies and municipalities needing accredited validation for digital portals.
Organisations looking for certified penetration testers Malaysia can also use a professional engagement to validate a new application, cloud deployment, or external attack surface. Typical triggers include an upcoming risk assessment or audit under Act 854, an ISO 27001 or BNM RMiT deadline, a pre-launch security check for a new application or cloud deployment, or a vendor risk assessment requested by an enterprise client.
BitRanger delivers this testing through a NACSA-licensed local cybersecurity team, going beyond automated scanning to show exactly how an attacker could chain small weaknesses into full domain control.
Why Automated Scanning Alone Is Not Enough
A lot of organisations assume that running a vulnerability scanner once a quarter satisfies their security obligations. It does not, and this is one of the common gaps BitRanger sees during client engagements.
- False sense of security: Automated scans generate false positives and miss the way attackers chain minor vulnerabilities together to gain full control of a network.
- Unclear business impact: Generic vendors hand over long, technical exploit dumps without explaining what it actually means for the business, which makes it hard for CISOs to justify budget to the board.
- Scarce local, certified expertise: Finding a trustworthy local penetration testing team with recognised offensive security certifications who also understand Malaysian compliance frameworks is genuinely difficult.
- Fear of downtime: Many organisations worry that aggressive testing will disrupt live production systems or industrial networks during business hours.
How BitRanger’s Penetration Testing Works
BitRanger structures every engagement around a clear scope, a controlled testing window, and a report the business side can actually use, not just the technical team. The approach is designed to give organisations a practical pentest service that validates security controls while keeping agreed operational boundaries in place.
Engagement formats
- Black-box testing: Testers start with zero prior knowledge, simulating how an external attacker would approach your systems from the outside.
- Grey-box testing: Testers are given standard user credentials to assess internal lateral movement and privilege escalation risk.
- White-box testing: Testers get full architecture and source code visibility for a deep, comprehensive assessment.
- Bundled retainer: Penetration testing can be combined with RAVEN vulnerability assessment and OwlSight SOC for continuous validation.
Standards and methodology
Testing is carried out under Rules of Engagement (RoE) and controlled exploitation windows to keep live operations running normally, and follows recognised frameworks including OWASP Top 10 for web and API security, OSSTMM (Open Source Security Testing Methodology Manual), and NIST SP 800-115.
What You Get From an Engagement
- Validated security posture: Confirmation of whether your existing firewalls, endpoint protection, and SOC alerting actually stop a skilled human attacker in real time.
- Demonstrated business impact: Clear proof of how a vulnerability could lead to financial loss, a data breach, or an operational halt, in language executives can act on.
- Compliance evidence: Documentation that supports your cyber security risk assessment and audit under Act 854, as well as BNM RMiT, ISO 27001 and data protection requirements.
- Prioritised remediation roadmap: Step-by-step technical guidance for your internal IT staff, ranked by business risk rather than a flat technical list.
- Post-remediation re-testing: Verification testing to confirm that the vulnerabilities identified were actually fixed, not just marked as closed.
Why Choose BitRanger for Penetration Testing
- NACSA-licensed: testing is conducted under BitRanger’s NACSA penetration testing licence (licence no. 20314-02, Act 854), so the results carry regulatory weight, not just technical value.
- Offensive and defensive synergy: attack insights from every engagement are fed back to tune OwlSight SOC and RAVEN vulnerability detection logic, so your defences actually improve after the test.
- Local, on-the-ground team: BitRanger’s testers operate out of Penang and understand the Malaysian regulatory and threat landscape, rather than working off a generic offshore playbook.
- Research backed methodology: BitRanger’s work is grounded in the same academic and applied research base as USM’s Cybersecurity Research Centre (CYRES).
Frequently Asked Questions
What is the difference between vulnerability assessment and penetration testing?
A vulnerability assessment scans your systems and lists known weaknesses. Penetration testing goes further: a human tester actively tries to exploit those weaknesses and chain them together to show real, demonstrable business impact, not just a list of flagged issues.
Is penetration testing mandatory in Malaysia?
The Cyber Security Act 2024 (Act 854) does not name penetration testing as such. Its duties apply to organisations designated as National Critical Information Infrastructure (NCII) entities, which can be government bodies or private companies in the 11 NCII sectors. An NCII entity must implement NACSA’s code of practice (section 21), carry out a cyber security risk assessment and have an audit done by a NACSA-approved auditor within the prescribed period (section 22), and notify cyber security incidents (section 23). Penetration testing is a practical way to produce the evidence those assessments and audits need.
The penalties are significant. Failing to implement the code of practice or to notify an incident can lead to a fine of up to RM500,000, imprisonment of up to ten years, or both. Failing to carry out the risk assessment or audit can lead to a fine of up to RM200,000, imprisonment of up to three years, or both. Under section 58, directors and officers can be held personally liable for offences committed by their company.
Will penetration testing disrupt my live systems?
BitRanger runs every engagement under agreed Rules of Engagement and controlled exploitation windows specifically to avoid disruption to live production systems, industrial networks, or critical web services during business hours.
How much does penetration testing cost?
Our products and services are priced on the number of assets, or the events per second, in your organisation. So we first hold a session to understand your requirements before giving you a quote. Reach out for an initial discussion, and we will work out the solution and pricing with you from there.
Get Started
If you have an Act 854, ISO 27001, or BNM RMiT deadline coming up, or you simply want proof that your defences hold against a real attacker, BitRanger’s NACSA-licensed penetration testing team can scope an engagement around your environment. Whether you need a pentest service for a web application, API, cloud environment, network, or internal infrastructure, BitRanger can discuss black-box, grey-box, or white-box testing for your organisation.